THE EXECUTION BOUNDARY PROBLEM
Why an Authorization Decision Is Not Proof of Authorized Action
Subtitle: Why Autonomous Enterprises Must Validate Authority at the Point of Execution, Not Merely at the Point of Approval.
Opinion · AI-assisted, human edited
Subtitle: Why Autonomous Enterprises Must Validate Authority at the Point of Execution, Not Merely at the Point of Approval.
Publication: AexoreX Newsroom Article Number: #075 Series: Enterprise Intelligence Infrastructure Research Category: Enterprise Intelligence · AI Governance · Authorization Architecture · Agentic Systems Security Article Type: Research & Analysis Author: AexoreX Research Desk Editorial Classification: Opinion · AI-assisted, human edited
---
Executive Summary
An enterprise system may approve an action correctly and still execute it under conditions that are no longer valid.
A purchase order may receive approval while a supplier remains eligible. Before the order is submitted, the supplier could be suspended, the budget could change, the approval could expire, or a policy revision could restrict the transaction.
The original authorization may have been valid when it was granted. That does not automatically establish that the resulting action remains authorized when execution occurs.
This distinction becomes increasingly important as enterprise systems evolve from applications that primarily record human decisions into interconnected environments where software agents can interpret objectives, coordinate workflows, invoke tools, and initiate actions across multiple services.
The challenge is not simply whether an AI system can make a reasonable decision. It is whether the enterprise can establish that a particular action was authorized under the applicable conditions when the action crossed the boundary into execution.
This is the execution boundary problem.
For autonomous enterprises, authorization must be more than a decision recorded earlier in a workflow. It must be enforced through the systems that perform consequential actions, with appropriate handling of changing context, delegated authority, concurrent operations, failures, and evidence.
This article examines the problem through established security concepts, distributed-systems considerations, and emerging research on AI agents. It also proposes an analytical framework—the Execution Authorization Envelope (EAE)—to help enterprise architects examine the conditions surrounding consequential execution.
EAE is a proposed framework for analysis, not an established industry standard or a validated implementation.
The central argument is straightforward:
A past authorization decision cannot, by itself, guarantee that a future action remains authorized.
The objective is not to eliminate autonomy. It is to make autonomy accountable to explicit enterprise authority.
---
1. From Authority Continuity to the Execution Boundary
In AexoreX Newsroom #074, Authority Continuity: The Missing Runtime Contract for Autonomous Enterprise Operations, the central question was how an enterprise can maintain a reliable connection between approved authority and the actions performed under it.
That discussion examined the relationship among identity, permissions, business decisions, execution controls, evidence, and reconciliation.
This article takes a narrower step.
Even when an enterprise has established a valid authority model, it must still answer a more specific question:
What must be verified immediately before a consequential operation is allowed to proceed?
Consider a procurement workflow.
An employee requests a purchase. The policy engine evaluates the request and permits it. An AI agent prepares the purchase order. Before submission, the supplier's status changes or a new policy takes effect.
If the downstream system relies solely on the earlier approval, it may execute an operation whose original conditions no longer hold.
This scenario is illustrative; it is not a claim that all procurement systems behave this way.
The important distinction is between maintaining authority throughout an operation and enforcing the relevant conditions at the point where an action is attempted.
The relationship can be expressed conceptually:
Authority Continuity → Execution-Time Validation → Controlled Execution → Evidence and Reconciliation
This is an analytical sequence, not a mandatory industry architecture.
Authority Continuity addresses the broader relationship between decisions and operations. Execution-time validation examines whether the applicable conditions are satisfied when a particular action is about to occur. Controlled execution enforces the relevant requirements. Evidence and reconciliation help establish what actually happened.
These concerns overlap, but they are not interchangeable.
A system may document an approval without checking whether it remains applicable. It may perform a runtime permission check without verifying a critical business condition. It may execute an operation successfully without establishing that the final business outcome was correct.
The execution boundary brings these questions into focus.
2. The Difference Between Intent, Capability, Authority, and Outcome
Autonomous enterprise architecture requires several concepts to remain distinct.
Intent describes what a person or system is trying to accomplish.
Capability describes what a component can technically do.
Authorization determines whether an operation is permitted under applicable rules and conditions.
Execution is the actual attempt to perform the operation.
Outcome describes the resulting state or effect.
These concepts are related, but none should be treated as a substitute for another.
An AI agent may be technically capable of submitting a payment without being authorized to submit a particular payment. A user may approve a transaction without authorizing every possible modification to it. A workflow may have been approved initially but later become ineligible because a relevant condition changed.
Likewise, a record stating that an operation was approved does not independently prove that the downstream system enforced the approval correctly.
The distinction matters because enterprise systems often distribute responsibility across multiple components.
An AI agent may interpret a request and prepare an action. An identity service may establish the caller's identity. A policy engine may evaluate permission. A workflow engine may coordinate the process. A separate application or external service may perform the final operation.
Each component may behave as designed while the overall process still contains a gap between the original authorization and the final action.
The architectural objective is therefore not merely to identify who requested an action or which permissions the caller possesses.
It is to establish that the operation being attempted falls within the authority applicable to that operation and that the relevant controls are enforced where they matter.
Capability does not establish authority. Prior approval does not establish continuing validity. Successful execution does not independently prove correct authorization.
3. The Time-of-Check to Time-of-Use Problem
A central technical concern at the execution boundary is the time-of-check to time-of-use problem, commonly abbreviated as TOCTOU.
TOCTOU occurs when a system checks a condition and then uses the result after the relevant state has changed.
For example, an application may check whether a resource is available, but another process may modify that resource before the application acts on the check.
The risk is not limited to AI. It is a longstanding concern in computer security and concurrent systems.
However, agentic workflows introduce additional questions because an AI agent may plan across multiple steps, consult external state, invoke several tools, and delay execution while processing information.
A check performed during planning may no longer reflect the conditions present when the planned action is attempted.
A 2025 research preprint, Mind the Gap: Time-of-Check to Time-of-Use Vulnerabilities in LLM-Enabled Agents, investigates this problem in LLM-enabled agents using a benchmark of 66 tasks and evaluates several possible mitigations. The work is relevant to this discussion, but its findings should be interpreted within the study's scope. A preprint does not establish that the same results apply to every production environment. (Research paper)
The architectural lesson is clear: checking a condition once does not necessarily guarantee that the condition remains true when the result is used.
Why a simple recheck may not be enough
Suppose a system checks that a purchase order is below a spending limit.
If the spending limit changes immediately after the check but before the order commits, the system may still act on stale information.
A second check can reduce the time between validation and use. It does not necessarily eliminate the race condition if the state can change again before execution.
Depending on the system, stronger coordination may require an atomic conditional update, a version check, an appropriate transaction mechanism, a lock, or another form of concurrency control.
The correct solution depends on the underlying system and the consequences of failure.
For this reason, execution-time authorization should not be described as a universal solution that automatically eliminates TOCTOU vulnerabilities.
It is one part of a broader design that must account for state changes and the actual guarantees provided by the execution mechanism.
4. What Existing Security Standards Contribute
The execution boundary problem builds on established security foundations. It does not require enterprises to discard existing identity, access-control, or authorization systems.
The more useful question is how these foundations contribute to the enforcement of authority at execution time.
Attribute-Based Access Control
NIST SP 800-162 describes Attribute-Based Access Control (ABAC), in which authorization decisions are determined by evaluating attributes associated with the subject, object, requested operation, and, where applicable, environmental conditions against relevant policies.
The appropriate reference is NIST SP 800-162, Guide to Attribute Based Access Control (ABAC) Definition and Considerations. (NIST)
ABAC provides a foundation for context-sensitive authorization.
However, an enterprise must still define where the evaluation occurs, which attributes matter, how changes are propagated, and whether the component performing the operation enforces the required decision.
The existence of an ABAC policy does not, by itself, prove that every downstream operation re-evaluates all relevant conditions at the appropriate time.
Zero Trust Architecture
NIST SP 800-207 describes Zero Trust Architecture as an approach that avoids granting implicit trust solely because a user, device, or resource resides within a particular network location or belongs to an organization.
The architecture focuses on protecting individual resources and explicitly evaluating access. (NIST SP 800-207)
This is relevant to autonomous enterprise systems because an AI agent should not receive unrestricted authority simply because it operates inside a trusted environment or has previously accessed a resource.
Yet Zero Trust is not, by itself, a complete answer to every execution-time authorization problem.
Business-level conditions, transaction state, concurrency, delegation, and uncertain execution outcomes may require additional controls.
OAuth 2.0 Token Exchange and Delegation
RFC 8693, OAuth 2.0 Token Exchange, defines a protocol for obtaining security tokens through an authorization server, including mechanisms involving impersonation and delegation. It is an IETF Standards Track specification. (RFC Editor)
Token exchange can help represent identity and delegated access across services.
However, token validity and business-level transaction eligibility are different questions.
A valid token may establish that a request satisfies certain identity and access requirements. It does not necessarily prove that a supplier remains eligible, that a purchase remains within the current budget, or that every business approval condition remains satisfied.
A related IETF proposal addresses delegated continuation in asynchronous and long-running workflows. As of October 21, 2026, the latest version listed is draft-zhu-oauth-async-delegation-05, titled Delegated Refresh Tokens for OAuth 2.0 Token Exchange. It remains an active Internet-Draft, not a finalized standard. (IETF Datatracker)
It is useful to distinguish such emerging work from specifications that have already been published as RFCs.
Agentic AI Security
The OWASP Top 10 for Agentic Applications 2026 provides a security-risk framework for autonomous and agentic AI systems. OWASP published it on December 9, 2025, following collaboration among industry experts, researchers, and practitioners. (OWASP)
The framework is useful for identifying and discussing agentic security risks.
It should not, however, be treated as proof that every listed risk occurs in every deployment or that a particular architecture eliminates those risks.
Together, these sources provide foundations for identity, access control, delegation, and AI risk management.
They do not remove the need to define exactly what must be true before a consequential action is allowed to proceed.
5. The Execution Boundary as an Enforcement Point
An execution boundary is the point at which a proposed operation becomes an attempt to change an enterprise resource or an external system.
Depending on the architecture, this may be an API endpoint, a transaction processor, a workflow action, a database operation, a payment service, or another controlled interface.
A large enterprise may have many such boundaries rather than one universal execution point.
The objective is to ensure that the component responsible for performing a consequential operation enforces the relevant authority requirements, either directly or through a trusted control mechanism.
A useful conceptual sequence is:
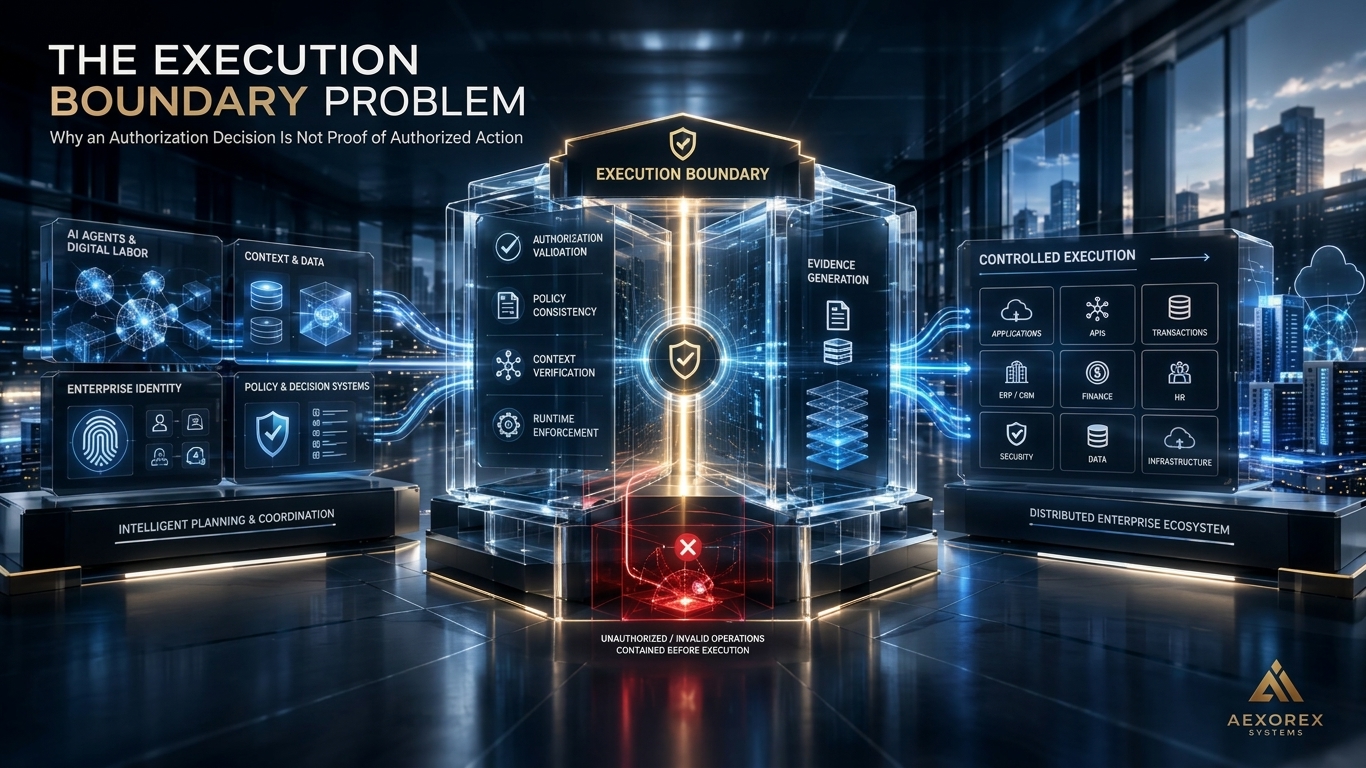
Request → Context Evaluation → Authorization → Execution-Time Validation → Controlled Execution → Evidence → Reconciliation
Each stage addresses a different question.
Stage Primary question
Request What operation is being proposed? Context evaluation What relevant conditions and constraints apply? Authorization Is the operation permitted under the applicable policy? Execution-time validation Are the required conditions still satisfied? Controlled execution Can the operation proceed within its permitted scope? Evidence What can be demonstrated about the decision and action? Reconciliation Did the expected outcome occur, and how are discrepancies handled?
This sequence is a conceptual model, not a mandatory implementation specification.
The appropriate controls depend on the system.
A database may support atomic conditional updates. An external API may not. A payment service may confirm a transaction synchronously, while another service may return an uncertain result after a timeout.
The design must therefore be explicit about which guarantees it can provide.
It should distinguish between validating authority, enforcing authority, and determining whether the intended business outcome actually occurred.
6. A Proposed Analytical Framework: Execution Authorization Envelope
To make the execution boundary easier to evaluate, this article proposes the Execution Authorization Envelope (EAE).
EAE is a proposed analytical framework for organizing the information, conditions, and controls surrounding a consequential operation.
It is not an established industry standard, a published protocol, or a validated implementation.
The purpose of the framework is to help enterprise architects ask consistent questions before allowing an operation to proceed.
An EAE-inspired design can be examined through ten elements.
Element Question
1. Operation identity What specific action is being requested? 2. Acting principal Which user, service, or agent is initiating the operation? 3. Authority source What policy, delegation, approval, or permission supports the action? 4. Scope and constraints Which resources, actions, limits, and conditions are permitted? 5. Policy and context Which policy version and relevant conditions govern the decision? 6. Delegation chain Is the operation performed on behalf of another principal, and what authority supports that relationship? 7. Validity conditions What must remain true for the operation to proceed? 8. Execution boundary Which component is responsible for enforcing the required controls? 9. Evidence What records connect authorization, validation, and the execution outcome? 10. Failure and reconciliation What happens when authority is invalid, execution fails, or the outcome is uncertain?
These elements do not prescribe a universal data structure or require every field to be transmitted in a single object.
Some information may be represented by references to authoritative policy records, identity services, transaction state, or approval systems.
The design must also account for confidentiality, data minimization, integrity, and the operational cost of additional checks.
Applying the framework
Consider a purchase order that was approved under a specific policy and a defined set of conditions.
Before submission, the execution component evaluates the conditions that the governing policy requires to remain valid.
If a required condition is no longer satisfied, the operation should be rejected, returned for renewed authorization, or escalated according to the applicable policy.
If the relevant state cannot be established, the system should follow an explicit uncertainty policy rather than silently interpreting missing information as permission.
If the operation proceeds, the system should record enough evidence to explain which controls were applied and what outcome was observed.
This example illustrates the intended reasoning process. It does not demonstrate that EAE has been implemented or validated in a production system.
The value of EAE lies in the questions it makes explicit, not in a claim that one universal envelope can eliminate all authorization failures.
7. Enforcement Must Extend Beyond Approval Records
An enterprise may maintain detailed approval records and still have inadequate execution controls.
Documentation helps explain what should have happened. Enforcement determines what the system is permitted to do.
A mature design needs both.
Enforce authority where the action occurs
The component performing a consequential operation should enforce the relevant authorization requirements, either directly or through a trusted mechanism.
An upstream AI agent should not be the sole authority responsible for deciding whether its own proposed action is permitted.
Separating planning from enforcement helps reduce reliance on an agent's interpretation of policy and creates a clearer boundary between reasoning and execution.
Bind authorization to the intended operation
Authorization should be sufficiently specific to the action it permits.
Depending on the use case, relevant details may include the target resource, operation type, transaction amount, intended recipient, or other material constraints.
If a previously approved action changes in a meaningful way, the system should determine whether the existing authorization still applies.
The required level of specificity depends on the operation's risk and the organization's governance requirements.
Handle changing conditions deliberately
The architecture should identify which conditions require validation at execution time and which can safely be evaluated earlier.
Where possible, validation and state changes should be coordinated through mechanisms appropriate to the underlying system.
An atomic conditional update may be suitable for one operation, while another may require a different transaction or concurrency-control strategy.
A final check without appropriate coordination may still leave a race condition.
Make revocation operationally meaningful
Revocation is useful only to the extent that it affects the relevant execution path.
The system should define how revoked authority is recognized, how pending actions are handled, and what happens when a downstream component cannot confirm the current state.
Revoking authority does not necessarily reverse an action that has already completed.
The design must distinguish between preventing future actions, stopping pending work, and recovering from completed or partially completed operations.
Design for uncertain outcomes
A request may fail before reaching the receiving system, fail after reaching it, or succeed without a confirmation reaching the caller.
The system should distinguish among:
- Rejected before execution.
- Confirmed execution.
- Confirmed failure.
- Outcome unknown and requiring reconciliation.
Idempotency mechanisms can help prevent duplicate effects when operations are retried. They do not independently establish authorization.
Similarly, an audit log can record what a system reports, but it does not guarantee that the underlying control operated correctly.
The architecture must combine the appropriate mechanisms rather than treating one control as a substitute for all the others.
8. Evidence Must Connect Authority to Actual Execution
Evidence is essential when an enterprise needs to explain why an operation was permitted and what happened afterward.
A useful evidence model distinguishes three questions.
Decision evidence: What authorization decision was made, under which policy and conditions?
Enforcement evidence: What validation and control checks occurred at the execution boundary?
Outcome evidence: Did the operation succeed, fail, or remain unresolved?
These records should be correlated through suitable identifiers so investigators can reconstruct the relevant sequence.
Depending on the operation, records may include timestamps, the identity of the acting component, an operation identifier, the applicable policy reference, validation results, and the downstream response.
However, the presence of a log entry is not proof that the underlying control operated correctly.
Evidence quality depends on the integrity of the records, the trustworthiness of their sources, the completeness of the event sequence, and the ability to connect recorded decisions to actual system behavior.
For sensitive enterprise operations, the design should also address access restrictions, retention, privacy, and protection against unauthorized alteration.
The NIST AI Risk Management Framework provides broader guidance for managing AI-related risks across the design, development, deployment, use, and evaluation of AI systems. Organizations should consult NIST's current publication information when using the framework for formal governance work. (NIST AI RMF)
The connection to execution authority is practical: governance expectations must be translated into controls that can be evaluated and evidence that can be examined.
9. Human Authority and Autonomous Operations
Autonomy does not require the removal of human authority.
For consequential operations, an enterprise may require human approval, separation of duties, escalation, or the ability to suspend a workflow.
These controls should be based on the operation's risk and the organization's governance requirements.
A useful design distinguishes between the ability to propose an action, the authority to approve it, the permission to execute it, and the ability to stop or contain an operation.
An AI agent may prepare a transaction without being permitted to approve it. A service may execute a transaction only after receiving the required authorization. A human supervisor may be empowered to suspend future operations when a relevant risk condition is detected.
The system should also define what a human override can actually accomplish.
Stopping future actions is different from reversing an action that has already completed. Suspending an agent does not necessarily cancel requests already accepted by downstream services. Revoking a token may not reverse an external transaction.
For that reason, human override must be designed around the actual execution architecture, including pending requests, downstream systems, and recovery procedures.
The goal is not simply to provide an emergency button.
It is to establish clear authority over what can proceed, what must stop, and what requires investigation or reconciliation.
10. An Evaluation Model for Enterprise Architects
Organizations evaluating autonomous workflows can use the following questions to identify potential gaps.
Evaluation area Core question
Authorization scope Is permission specific enough for the operation being performed? Context validity Which conditions must still be true when execution begins? Enforcement Which component actually prevents an unauthorized operation? Delegation Can the enterprise trace the authority behind actions performed by downstream agents or services? Revocation How are revoked permissions and changed policies reflected in pending workflows? Concurrency Can the relevant state change between validation and execution? Failure handling How are retries, duplicate effects, partial failures, and uncertain outcomes managed? Evidence Can investigators connect the authorization decision to the actual execution outcome? Human control Who can approve, suspend, escalate, or contain the operation? Testing Have relevant failure scenarios been tested under realistic conditions?
This model is not a certification checklist or a substitute for a formal security assessment.
Its purpose is to help enterprise architects identify where authorization assumptions may be stronger than the controls actually implemented.
The evaluation should be performed against the system's real architecture, including identity services, policy engines, APIs, databases, workflow orchestrators, and external dependencies.
A design that works for an internal database transaction may not be sufficient for an operation spanning several independent organizations.
11. The Long-Term Direction: From Permission Records to Governed Execution
The execution boundary problem is likely to remain relevant as enterprises adopt more sophisticated automation, agentic workflows, and multi-system orchestration.
The following horizons are strategic scenarios, not predictions of guaranteed industry milestones.
Near term: Make existing authority enforceable
Organizations can begin by mapping consequential actions, identifying their execution points, and determining which authorization conditions must remain valid.
Priority areas include service identity, narrowly scoped permissions, revocation handling, evidence collection, failure management, and testing of changes between approval and execution.
The objective is to expose gaps between documented policy and actual system behavior.
Medium term: Improve coordination across agents and services
As workflows span more components, organizations may need more consistent ways to represent delegation, validate changing conditions, correlate evidence, and reconcile outcomes.
Interoperability will matter, but it should not be confused with uniformity: different services may require different enforcement and transaction mechanisms.
Standards and emerging proposals may contribute to these efforts, but enterprises should distinguish finalized specifications from work in progress.
Long term: Treat execution authority as an enterprise-wide architectural concern
A more autonomous enterprise may coordinate many agents, services, and business processes while retaining clear boundaries around what each component is permitted to do.
The enduring requirement is not that every action must be approved manually.
It is that autonomous execution remains bounded by explicit authority, enforceable constraints, and evidence sufficient for oversight.
The architecture should allow appropriate actions to proceed efficiently while ensuring that actions outside permitted boundaries are rejected, contained, or escalated.
The long-term objective is governed autonomy: systems that can operate with increasing independence without making authority ambiguous or accountability impossible.
12. Implications for Enterprise Intelligence Infrastructure
Enterprise intelligence infrastructure must address more than the ability to interpret information and coordinate work.
It must also account for how decisions become actions, where authority is enforced, how delegated operations remain constrained, and how outcomes can be verified.
This creates a useful architectural distinction between intelligence and authority.
Intelligence may help a system interpret a request, evaluate options, and plan a workflow.
Authority determines which operations are permitted.
Execution controls enforce those permissions against the relevant system state.
Evidence supports the reconstruction and evaluation of what actually occurred.
These responsibilities may be implemented through several components rather than a single platform. The critical requirement is that their responsibilities and interfaces are clearly defined.
For AexoreX Systems, this is a relevant conceptual direction for research into enterprise intelligence infrastructure. It aligns with the broader architectural proposition behind AEOS QUANTUM: enterprise systems should not merely connect and orchestrate capabilities; they should also account for the authority governing the use of those capabilities.
This is a design direction, not proof of an implemented or independently validated capability.
Any future implementation would need to demonstrate its behavior through architecture documentation, security analysis, integration testing, failure testing, and other appropriate forms of verification.
The distinction matters because enterprise trust should be based on observable controls and evidence—not on architectural language alone.
Conclusion: Authority Must Survive the Journey to Execution
An authorization decision is an important event in an enterprise workflow. It is not, by itself, a guarantee that every later action remains authorized.
Between approval and execution, context may change, authority may be revoked, delegated components may introduce new boundaries, and distributed systems may produce uncertain outcomes.
The execution boundary is where these concerns become operational.
A reliable architecture must identify which conditions govern an action, enforce those conditions at the appropriate point, handle changes and failures deliberately, and produce evidence that connects the authorization decision to the resulting operation.
The proposed Execution Authorization Envelope offers one way to structure this analysis. Its value lies in the questions it makes explicit, not in any claim that it is already a recognized standard or a proven universal solution.
As enterprises become more autonomous, the essential design challenge will not simply be enabling systems to act.
It will be ensuring that their actions remain within the authority the enterprise has actually granted.
Autonomy determines how independently a system can operate. Governance determines the boundaries within which it may operate. Execution enforcement connects the two.
For the autonomous enterprise, authority must be more than approved.
It must be applicable, enforceable, and evidenced at the point of execution.
---
Research and Reference Notes
The following sources support specific aspects of the discussion. They do not collectively validate the proposed EAE framework.
1. NIST SP 800-162 — Guide to Attribute Based Access Control (ABAC) Definition and Considerations https://csrc.nist.gov/pubs/sp/800/162/upd2/final
2. NIST SP 800-207 — Zero Trust Architecture https://www.nist.gov/publications/zero-trust-architecture
3. IETF RFC 8693 — OAuth 2.0 Token Exchange https://www.rfc-editor.org/rfc/rfc8693.html
4. IETF Internet-Draft — Delegated Refresh Tokens for OAuth 2.0 Token Exchange https://datatracker.ietf.org/doc/draft-zhu-oauth-async-delegation/ Status: Active Internet-Draft; not a finalized IETF standard.
5. OWASP Top 10 for Agentic Applications 2026 https://genai.owasp.org/resource/owasp-top-10-for-agentic-applications-for-2026/
6. Lilienthal, D. & Hong, S. — Mind the Gap: Time-of-Check to Time-of-Use Vulnerabilities in LLM-Enabled Agents (2025) https://arxiv.org/abs/2508.17155 Research preprint; interpret findings within the study's scope.
7. NIST AI Risk Management Framework https://www.nist.gov/itl/ai-risk-management-framework Consult the current publication information before using the framework for formal governance work.
Related AexoreX Newsroom Research
- #071 — The Runtime Authority Problem: From Granted Permissions to Enforced Execution Boundaries
- #073 — The Authority Drift Problem: When Runtime Enforcement No Longer Matches Business Intent
- #074 — Authority Continuity: The Missing Runtime Contract for Autonomous Enterprise Operations
These articles provide the editorial context for the present discussion. #075 narrows the focus to the technical boundary between authorization evaluation and execution.
---
Editorial and Status Note
This article presents conceptual research and architectural analysis.
The Execution Authorization Envelope (EAE) is a proposed analytical framework for discussion and further evaluation. It is not represented as an established industry standard, certified methodology, or validated AEOS QUANTUM feature.
Examples are illustrative. The article does not claim that AexoreX Systems or AEOS QUANTUM has implemented, deployed, or independently validated all capabilities discussed.
The referenced standards and research support specific aspects of identity, access management, token handling, AI security, and execution risks. They should not be interpreted as direct proof of the proposed framework as a whole.
— AexoreX Research Desk The Intelligence, Research & Institutional Publication of AexoreX Systems
---
4. Paket SEO dan publikasi
Gunakan metadata berikut saat memasukkan artikel ke CMS AexoreX Newsroom.
Elemen Nilai final
Article number #075 SEO title The Execution Boundary Problem | AexoreX Newsroom URL slug the-execution-boundary-problem Meta description Why autonomous enterprises must validate authority at execution time. Explore runtime authorization, delegated AI actions, and enterprise governance. Primary keyword execution boundary problem Secondary keywords runtime authorization, AI agent security, execution-time validation, enterprise AI governance, delegated authority Article category Enterprise Intelligence Research Secondary categories AI Governance, Agentic Systems Security Article type Research & Analysis Author AexoreX Research Desk Editorial label Opinion · AI-assisted, human edited Language English (international)
Catatan: slug dan metadata ini merupakan rekomendasi siap digunakan. Keduanya belum berarti halaman website telah diperbarui.
Rekomendasi gambar utama
Image concept: The Enterprise Execution Boundary
Gambarkan arsitektur enterprise modern yang menghubungkan AI agents, identity and policy services, execution controls, serta evidence and reconciliation. Tempatkan execution boundary sebagai titik kontrol yang jelas di antara keputusan dan tindakan.
Hindari visual robot futuristis yang terlalu dekoratif. Gunakan gaya editorial teknologi enterprise: bersih, presisi, profesional, dan mudah dipahami.
Suggested image alt text:
Enterprise AI execution boundary showing authorization validation, controlled execution, and evidence verification.
Suggested image caption:
Autonomous enterprise systems require enforceable authority at the execution boundary, supported by evidence and outcome verification.
CTA untuk bagian akhir artikel
Explore the Future of Enterprise Intelligence Infrastructure
Discover how governed execution, delegated authority, and evidence-based control can shape the next generation of autonomous enterprise systems.
Explore AexoreX Systems: https://aexorex.com/
Read more from AexoreX Newsroom: https://news.aexorex.com/
Sources and attribution
- NIST, IETF, OWASP, and academic research papers cited in this article. References include NIST SP 800-162, NIST SP 800-207, OAuth 2.0 Token Exchange (RFC 8693), the OWASP Top 10 for Agentic Applications 2026, and relevant research on time-of-check to time-of-use vulnerabilities in AI agents. · statement link
About the author
Research desk of AexoreX Newsroom.
More from AexoreX Research Desk →Related stories
- From Agent Interoperability to Governed Execution: Why Enterprise AI Needs an Authority Layer
- AFTER REVOCATION: THE SAFE-STATE PROBLEM IN AUTONOMOUS ENTERPRISE EXECUTION
- From Access Grants to Executable Authority: Closing the Transaction-Boundary Gap in Agentic Enterprises
- THE EXECUTION CONTINUITY PROBLEM
- The Reconciliation Authority Problem
- The Runtime Authority Problem: From Granted Permissions to Enforced Execution Boundaries
- The Agent Factory Problem: Governing AI Systems That Create and Evolve Other Agents
- The Authority Drift Problem: When Runtime Enforcement No Longer Matches Business Intent