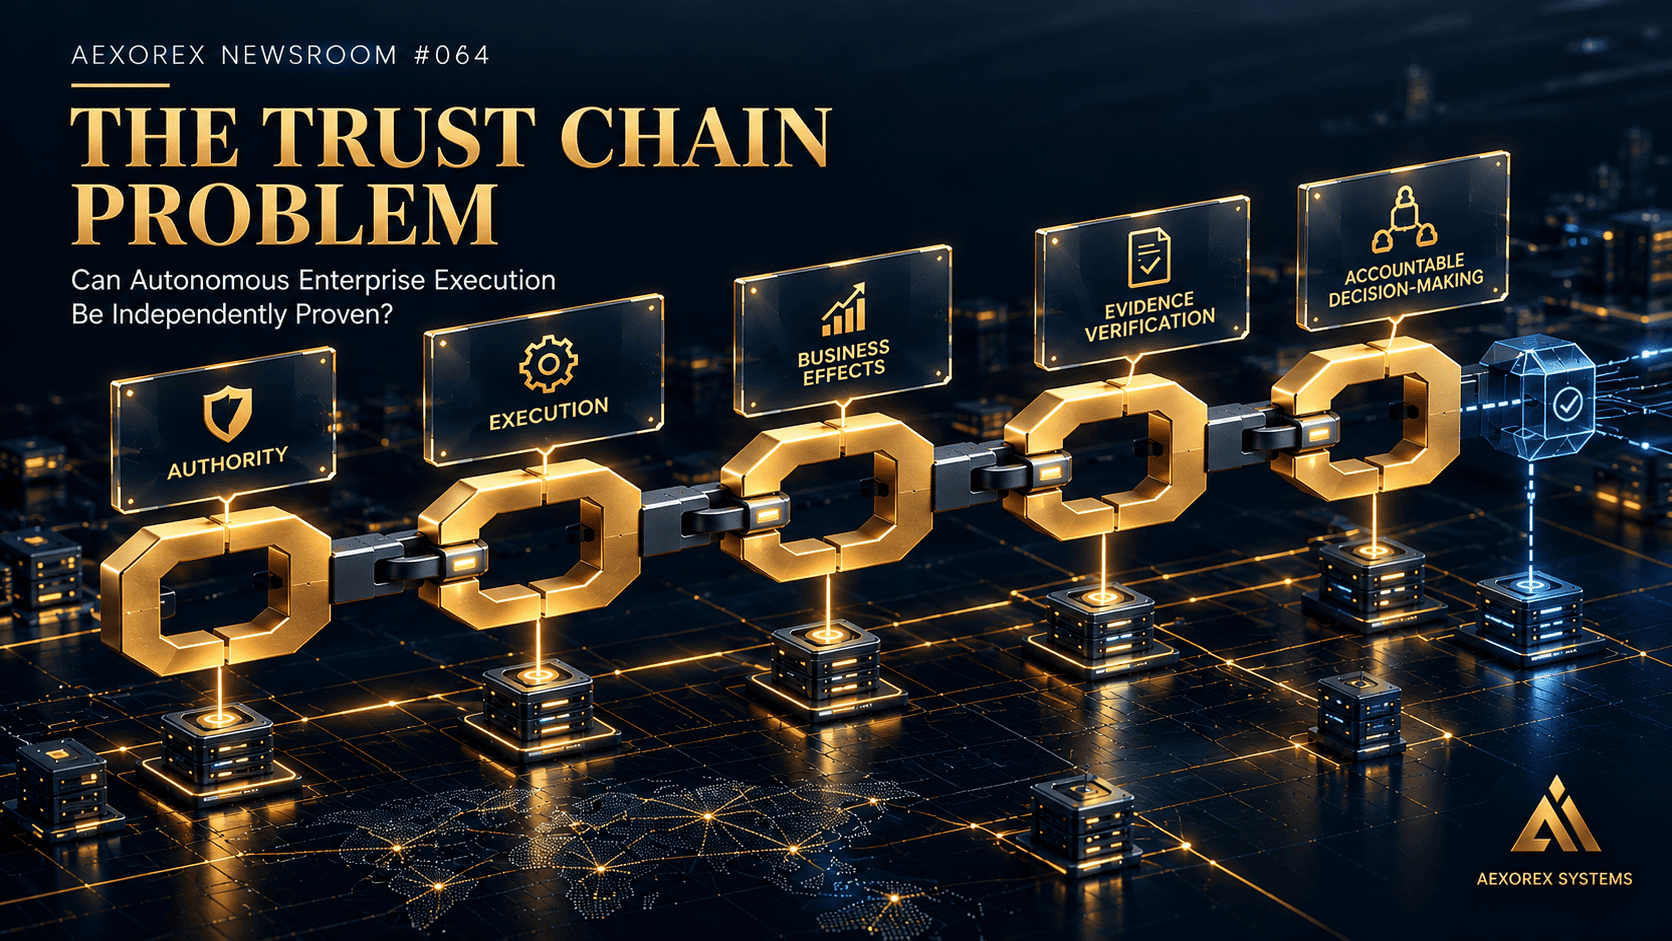
THE TRUST CHAIN PROBLEM
Can Autonomous Enterprise Execution Be Independently Proven?
AexoreX Newsroom proposes the Trust Chain Assurance Model, a conceptual framework to help enterprises evaluate evidence from diverse systems about autonomous operations and their effects.
Opinion · AI-assisted, human edited
EXECUTIVE SUMMARY
As artificial intelligence (AI) progresses from providing recommendations to directly interacting with enterprise applications, coordinating workflows, and initiating business operations, organizations confront a core challenge: How can an enterprise definitively determine what an autonomous system actually did, what lingering effects remain, and whether the available evidence sufficiently supports its conclusions?
Revoking an agent's authority does not automatically guarantee that all its operations have ceased. Confirming a workflow's termination does not necessarily mean all resulting business effects have been resolved. Simply collecting operational records does not ensure those records offer a complete or independently verifiable account of events. These are distinct problems, each demanding specific forms of evidence.
AexoreX Newsroom #062 previously explored the gap between authorization and containment. Report #063 extended this analysis to the difficulty of establishing a known operational state after authority revocation. This report advances the research to address the next crucial question: What constitutes sufficient evidence to support a defensible conclusion regarding autonomous enterprise execution?
This report proposes a conceptual framework called the Trust Chain Assurance Model. This framework examines six interconnected areas: operational context, evidence provenance, event correlation, claim-specific verification, bounded assurance, and accountable decision-making.
The model is a research proposal, not an established industry standard or a validated assurance methodology. Its primary purpose is to structure the questions an enterprise should address when evaluating evidence across diverse, interconnected systems.
Existing technologies offer important capabilities, including identity records, application logs, distributed tracing, cryptographic integrity mechanisms, and AI risk-management frameworks. However, these capabilities do not automatically combine to form a complete account of every operation and its consequences. The challenge lies in understanding what each source *can* establish, what it *cannot* establish, and how multiple sources can collectively support a conclusion without obscuring uncertainties.
For AEOS QUANTUM, this research identifies a potential architectural direction: coordinating evidence from heterogeneous enterprise systems, relating it to authorized operations, highlighting unresolved questions, and preserving human accountability for high-consequence decisions. The objective is not to promise absolute proof or eliminate all uncertainty but to help enterprises make more precise, evidence-based claims about the behavior of autonomous systems.
1. THE UNRESOLVED QUESTION AFTER REVOCATION
Consider an enterprise revoking an AI agent's authority to perform a business operation. The authorization system logs the revocation, and the organization expects the agent to cease activity. However, what happens to operations already initiated?
A request may have reached an external service, a workflow might be processing asynchronously, or a business application could have accepted an instruction before the revocation took effect. A downstream system might still be processing a previously submitted request. These scenarios are possible in distributed architectures, and their relevance depends on the specific systems and how they manage authorization, execution, cancellation, and completion.
The core issue is that changing an authorization state, by itself, does not establish the status of every operation associated with that authority. This problem was the focus of previous research.
- #062 — The Containment Gap investigated why authorization does not automatically guarantee containment and why an agent's self-report should not be treated as independent evidence.
- https://news.aexorex.com/news/the-containment-gap
- #063 — After Revocation: The Safe-State Problem in Autonomous Enterprise Execution extended this analysis to the challenge of establishing the state of execution and business effects following authority revocation.
- https://news.aexorex.com/news/after-revocation-the-safe-state-problem-in-autonomous-enterprise-execution
This report continues that investigation. Suppose an organization collects records from its identity provider, workflow engine, business applications, and monitoring infrastructure. Can it then establish that the agent stopped, whether an operation completed, whether the relevant business state changed, and if any outstanding effects remain? Furthermore, can an authorized reviewer independently examine the evidence supporting these conclusions?
These questions cannot always be answered solely by collecting more logs. The organization must evaluate whether the available records are relevant, reliable, sufficiently complete, and directly connected to the specific claim under investigation. The challenge is not merely to gather evidence but to determine what that evidence genuinely allows the enterprise to claim to know.
2. FOUR DISTINCT DIMENSIONS OF OPERATIONAL ASSURANCE
A useful starting point is to differentiate four dimensions often treated as interchangeable:
**Dimension: Authority** *Core question:* Was the operation permitted under the applicable authorization rules? *What it does not automatically establish:* That the operation executed correctly or stopped when required.
**Dimension: Execution** *Core question:* Was the operation initiated, accepted, completed, canceled, or left unresolved? *What it does not automatically establish:* That every resulting business effect has been resolved.
**Dimension: Effect** *Core question:* What relevant change occurred in the affected business systems? *What it does not automatically establish:* That every related system has reached the intended state.
**Dimension: Evidence** *Core question:* What supports each conclusion, and how reliably can that information be evaluated? *What it does not automatically establish:* That every relevant event was observed or that the conclusion is universally true.
These dimensions are related, but evidence pertaining to one does not automatically prove the others. For instance, an authorization record may confirm permission withdrawal but not necessarily that an already accepted operation was canceled. A workflow record may show task termination but not whether the task had already altered a business record. A business application reporting a committed change may not indicate whether every downstream process has completed.
Similarly, an authentic record can accurately describe one event but remain insufficient to support a broader operational conclusion. This distinction leads to a foundational principle: evidence must be evaluated against the precise claim it is intended to support. The scope of the claim dictates the relevance of evidence, the necessary verification, and the limitations that must be disclosed.
3. WHAT EXISTING TECHNOLOGIES ALREADY PROVIDE
The Trust Chain Problem does not imply a complete lack of necessary technologies within enterprises. Important components already exist; the challenge is to understand their individual capabilities and how they can contribute to a defensible assessment.
3.1 Identity and authorization systems
Identity and authorization systems provide records of identities, access grants, policy decisions, credential changes, and revocation events. These records help establish what the relevant system recorded about an authorization decision. However, an authorization record does not necessarily establish the status of every operation already initiated or accepted by another system. The enterprise must differentiate between the authorization state and the execution state.
3.2 Application and workflow systems
Business applications and workflow engines can record requests, processing stages, errors, retries, state changes, and completion events. These records can provide crucial evidence about an operation's lifecycle. Their meaning, however, depends on the system's semantics. For example, an acknowledgment that a request was accepted is not necessarily equivalent to confirmation that the requested business change was committed. Similarly, a workflow termination event does not automatically establish the final state of every downstream dependency. Therefore, the precise meaning of each recorded event must be understood before it is used to support a broader conclusion.
3.3 Monitoring and distributed tracing
Monitoring and tracing technologies assist operators in examining system activity, dependencies, timing, failures, and relationships between recorded events. They can offer valuable operational context. However, observability is not equivalent to complete knowledge. A monitoring system can only report what it observes through its available instrumentation and data sources. A trace can connect recorded operations without necessarily confirming that every relevant event or downstream effect has been captured. Consequently, the absence of an alert or trace entry should not automatically be interpreted as proof that no relevant activity occurred.
3.4 Cryptographic integrity and provenance
Cryptographic mechanisms can help establish properties such as data integrity, the relationship between signed content and a signing key, or the continuity of a defined evidence sequence. These properties can strengthen an evidence trail. However, cryptographic integrity does not independently guarantee the truthfulness of the original information, that every relevant event was recorded, or that the underlying business state was accurately represented. The integrity of a record and the truth of the claim described by that record are distinct properties. An authentic record can faithfully preserve an incomplete observation, and a signed statement can establish its signer without automatically validating every assertion within it.
3.5 AI risk management and governance
The National Institute of Standards and Technology (NIST) offers two relevant resources: - Artificial Intelligence Risk Management Framework (AI RMF 1.0), published in January 2023. - Artificial Intelligence Risk Management Framework: Generative Artificial Intelligence Profile, published as NIST AI 600-1 in July 2024.
These publications provide guidance for identifying, assessing, and managing AI-related risks, covering governance, documentation, evaluation, monitoring, and organizational accountability.
Sources: NIST AI RMF 1.0 NIST AI 600-1: Generative AI Profile
These resources support the broader governance context of this research. They should not be interpreted as validating the Trust Chain Assurance Model or as establishing a universal solution for independently verifying every post-revocation business effect across heterogeneous enterprise systems. Governance frameworks, evidence technologies, and operational coordination are complementary but distinct concerns.
4. THE PROVENANCE BOUNDARY: WHOSE ACCOUNT ARE WE TRUSTING?
Consider an AI agent reporting: "My execution has stopped, and the requested operation is complete." This statement may provide useful information, but its evidentiary value depends on what the agent can observe and how its report can be corroborated.
The agent may know its own process terminated without knowing if an external service is still processing a request. It may know a request was accepted without knowing if the requested business change was committed. It may also lack visibility into downstream systems.
The appropriate response is not to assume every agent report is false. Instead, it is to distinguish between a system's reported status and a status established through appropriate verification. Depending on the claim, an enterprise may need evidence from several sources: - The identity provider records the authorization change. - The workflow engine records the execution state. - The target application reports the relevant business-object state. - A downstream service provides evidence about a dependent operation. - Monitoring records provide additional information about observed activity.
These sources can offer complementary views of an operation. However, the number of sources alone does not measure assurance. Multiple systems may rely on the same underlying information, several records might repeat one original report, or two systems might use different definitions of "completion." Different records may also contradict each other.
A meaningful assessment therefore needs to consider the following questions: - **Provenance:** Where did the evidence originate? - **Integrity:** What supports confidence that the evidence has not been altered? - **Semantics:** What does the recorded event actually mean? - **Correlation:** Can the record be reliably associated with the operation under investigation? - **Coverage:** Which systems, events, and time intervals are represented? - **Independence:** Does the additional evidence provide a genuinely separate basis for the conclusion? - **Limitations:** What cannot be established from the available information?
These questions also arise in existing work on verifiable AI provenance. For instance, the Verifiable AI Provenance Framework Internet-Draft discusses approaches to provenance and verifiable decision trails. The cited document is an individual Internet-Draft, not an IETF-endorsed standard.
Reference: https://datatracker.ietf.org/doc/draft-kamimura-vap-framework/
AexoreX does not claim to have invented provenance, cryptographic integrity, independent verification, or the general idea of linking evidence to decisions. The specific research question here is narrower: How can an enterprise evaluate evidence from different systems against defined claims about authority revocation, distributed execution, and business-effect resolution? This is the operational problem central to this report.
5. THE PROPOSED TRUST CHAIN ASSURANCE MODEL
AexoreX Newsroom proposes the Trust Chain Assurance Model as a conceptual framework for further research. The model is designed to help structure the assessment of evidence across interconnected enterprise systems. It is not presented as an established industry standard, a validated assurance methodology, or a claim of existing AEOS QUANTUM functionality.
5.1 The conceptual architecture
**Operational Context → Evidence Provenance → Event Correlation → Claim-Specific Verification → Bounded Assurance → Accountable Decision**
These components are related but do not necessarily operate in a rigid sequence. Verification may reveal missing evidence, require additional correlation, or expose contradictions that necessitate further investigation. Therefore, the process should be understood as iterative.
**Component: Operational context** *Core question:* What operation, authority, and relevant conditions are being examined? *Intended purpose:* Define the investigation's scope.
**Component: Evidence provenance** *Core question:* Where did each record originate? *Intended purpose:* Evaluate the source and its evidentiary properties.
**Component: Event correlation** *Core question:* Which records relate to the same operation or effect? *Intended purpose:* Connect relevant evidence across systems.
**Component: Claim-specific verification** *Core question:* Does the evidence meet the criteria for a particular claim? *Intended purpose:* Evaluate whether the conclusion is supported.
**Component: Bounded assurance** *Core question:* What can be concluded, within what scope, and with what limitations? *Intended purpose:* Prevent unsupported or overly broad conclusions.
**Component: Accountable decision** *Core question:* Who has the authority to accept the assessment and determine the next action? *Intended purpose:* Preserve responsibility for consequential decisions.
5.2 Evidence provenance
The first task is to understand where the evidence originated and what it represents. Depending on the system and the claim, a useful evidence record may include: - Source system and relevant record identifier. - Event type and the business object or operation concerned. - Event time and evidence-collection time, where available. - Identity of the system or service that produced the record. - Relevant correlation identifiers. - Integrity or authenticity mechanisms. - Known gaps and limitations.
These are potential design considerations, not a universal checklist that every system can satisfy. Some sources will provide more information than others. Missing fields or unavailable records should be treated as limitations, not silently assumed to exist.
5.3 Event correlation
The next task is to determine whether records refer to the same operation. One business action may generate multiple events across different services. These events may use different identifiers, represent different processing stages, or be recorded at different times. Correlation can help connect an authorization decision, an execution request, a workflow event, and a resulting business-state change.
However, correlation is not proof of causation. Two events occurring close together may be unrelated. Two records sharing an identifier may represent different stages of processing. Timestamp differences may reflect asynchronous execution, clock variation, or different recording conventions. Therefore, the correlation method must be appropriate for the claim and its technical context.
5.4 Claim-specific verification
Verification must begin with a clearly defined claim. Consider three statements: - The agent's authority was revoked. - All identified operations initiated under that authority have stopped. - All relevant business effects have been resolved.
These statements make progressively broader assertions. The first may be supported by evidence from the authoritative authorization system. The second may require evidence from execution environments, workflow engines, queues, and external services. The third may require evidence from the relevant business applications and dependent systems, along with an explicit definition of which effects must be resolved.
Evidence supporting the first statement does not automatically support the second or third. The broader the claim, the more carefully the enterprise must define its scope, assumptions, and verification criteria.
6. EVIDENCE STATES: WHAT DOES THE ENTERPRISE ACTUALLY KNOW?
Operational assurance should not force every investigation into a simplistic binary status. An enterprise may have enough evidence to verify a narrow claim, insufficient information to reach a conclusion, or credible records that disagree. To make these distinctions more explicit, AexoreX proposes the following evidence-state vocabulary for further research. These labels are proposed terminology, not a universal industry standard.
**Proposed state: VERIFIED** *Definition:* The claim satisfies predefined verification criteria within a stated scope and under stated assumptions. *Interpretation:* The specific claim is supported to the defined level.
**Proposed state: NOT VERIFIED** *Definition:* Verification was attempted, but one or more required criteria were not satisfied. *Interpretation:* The claim has not met the conditions required for acceptance.
**Proposed state: INDETERMINATE** *Definition:* Available evidence cannot establish whether the claim is true or false. *Interpretation:* The conclusion remains unresolved.
**Proposed state: CONTRADICTORY** *Definition:* Credible evidence sources materially disagree about the claim. *Interpretation:* The conflict requires investigation or an explicit decision about how it will be handled.
**Proposed state: INSUFFICIENT EVIDENCE** *Definition:* Required evidence is missing, incomplete, or inadequate for the planned verification. *Interpretation:* The evidence base does not meet the minimum requirements.
The definitions are important. "NOT VERIFIED" does not simply mean evidence is unavailable; it indicates that verification was attempted, and the defined criteria were not met. "INSUFFICIENT EVIDENCE" describes a deficiency in the available evidence, which may lead to an "INDETERMINATE" conclusion. "CONTRADICTORY" identifies a material conflict between credible sources; further investigation may resolve it, but it should not be hidden behind an apparently successful status.
These states are not necessarily points on a single scale; they describe different evidentiary conditions. Most importantly, "VERIFIED" applies to a specific claim, not automatically to the entire enterprise system. Verification that an authorization was revoked does not establish that every operation has stopped. Verification that one workflow terminated does not establish that every downstream effect has been resolved. Verification of one business record does not establish that every dependent system is consistent.
An evidence assessment should therefore communicate the claim, scope, criteria, relevant time, and known limitations alongside the status. The purpose is not to manufacture certainty but to make the actual state of knowledge explicit.
7. THE COMPLETENESS PROBLEM
Even authentic, well-correlated evidence may be insufficient if it does not cover the full scope of the claim. Suppose an enterprise receives records showing that three services completed their assigned tasks. Can the organization conclude that the entire business operation has completed successfully? Only if the relevant scope and completion criteria justify that conclusion.
A fourth service may have been involved but failed to provide evidence. A downstream event may still be processing. A retry may have occurred under a different identifier. An external provider may have accepted a request without confirming its final state. These are possible conditions, not assumptions about every enterprise environment. They demonstrate why evidence completeness must be assessed rather than presumed.
This problem becomes particularly important when a claim includes absolute terms such as: - All operations have stopped. - Every downstream effect has been resolved. - No relevant activity remains. - The environment is completely contained. - The enterprise has fully returned to a safe state.
Such claims impose a broader evidentiary burden than statements about a single event or business object. An enterprise may have strong evidence for one system but limited visibility into another. It may establish that identified workflows terminated without being able to establish the absence of every possible downstream effect. A defensible conclusion should preserve those boundaries.
For example: "Evidence confirms that the identified workflow terminated and that the target application reports the expected business-record state. The available evidence does not independently establish that every downstream dependency has completed processing." This statement is more limited than declaring the entire environment safe. It is also more informative because it identifies what has been established and what remains unresolved.
The absence-of-evidence problem
The absence of a recorded event does not automatically establish that the event did not occur. Such an inference requires a justified basis for believing that the relevant event would have been captured, retained, and made available under the conditions being examined.
An enterprise should therefore consider: - Whether the relevant system was expected to produce a record. - Whether the evidence-collection mechanism was operating during the relevant period. - Whether the source is authoritative for the claim. - Whether known collection or retention gaps exist. - Whether the operation could have occurred outside the observed path. - Whether the observation period is sufficient for the conclusion.
These questions cannot guarantee complete knowledge. They help define what can reasonably be inferred from the evidence available.
8. FROM SAFE-STATE CLAIMS TO BOUNDED ASSURANCE
The phrase "safe state" can be misleading if the organization has not defined what safety means for the operation under examination. For one workflow, the relevant condition may be that no new operation can be initiated under revoked authority. For another, the condition may require that in-flight operations have been canceled or completed. For a financial process, the organization may need to reconcile transactions and identify unresolved operations within a defined scope. For a data-management process, the organization may need to confirm the intended record state and assess dependent systems.
These are different operational requirements. The organization must therefore define the target state before attempting to verify that it has been reached. AexoreX proposes a Bounded Assurance Statement as a possible way to communicate the result of such an assessment.
A statement of this kind could include six elements: 1. **Claim:** What precisely is being asserted? 2. **Scope:** Which systems, operations, business objects, and time intervals are included? 3. **Evidence:** Which records or observations support the claim? 4. **Verification criteria:** What conditions must be satisfied for the claim to be accepted? 5. **Limitations:** What remains unknown, excluded, or dependent on assumptions? 6. **Decision and accountability:** Who is authorized to accept the assessment and determine the next action?
For example: - **Claim:** The identified workflow terminated following authority revocation. - **Scope:** The named workflow instance and its recorded execution environment. - **Evidence:** The workflow engine's termination record and associated execution-status evidence. - **Verification criteria:** The defined termination conditions have been satisfied for the identified workflow instance. - **Limitations:** The evidence does not independently establish the final state of every downstream business effect. - **Decision:** The responsible operator determines whether additional investigation or remediation is required.
This example illustrates the proposed structure; it is not a universal template that guarantees safety. The criteria must be appropriate to the operation, its risks, and the relevant enterprise policies. Bounded assurance does not mean accepting weak evidence; it means stating the conclusion at the level the evidence can support.
9. THE TRUST CHAIN AND ITS FAILURE CONDITIONS
A chain of evidence may contain authentic records, reliable timestamps, cryptographic protections, and detailed operational logs. Yet, the resulting conclusion may remain weak if a critical link is missing.
Consider five hypothetical conditions:
**Condition A — Authority is established, but execution is unknown.** The authorization system confirms revocation, but the enterprise cannot establish whether an already accepted operation continued.
**Condition B — Execution is established, but the effect is unknown.** The workflow engine reports termination, but the target application has not confirmed the final business state.
**Condition C — The effect is reported, but attribution is unclear.** A business record appears to have changed, but the available evidence does not reliably establish which operation produced the change.
**Condition D — Individual records are authentic, but their relationship is uncertain.** Several systems provide valid records, but the enterprise cannot confidently determine whether they refer to the same operation.
**Condition E — The identified operation is resolved, but evidence coverage is incomplete.** The known workflow has finished, but the enterprise has not established whether every relevant dependent operation has been considered.
Each condition represents a different limitation and may require a different response. Depending on the circumstances, the organization may need additional evidence, reconciliation, further observation, remediation, or escalation to an authorized decision-maker.
The central point is that no single technical property automatically resolves every evidentiary problem. Cryptographic integrity cannot establish completeness by itself. Correlation cannot establish causation by itself. An authentic source cannot automatically establish every fact outside its area of observation. A defensible conclusion depends on the relationship between the claim, the evidence, the verification criteria, and the scope of the assessment. This is why the proposed model treats provenance, correlation, verification, and accountability as distinct concerns.
10. IMPLICATIONS FOR AEOS QUANTUM
AEOS QUANTUM is envisioned as an enterprise intelligence and operations coordination platform. Its architectural principle is to connect, orchestrate, govern, and activate the enterprise stack rather than replace every underlying system. Within this direction, the Trust Chain Problem identifies a potential role for an enterprise-level evidence coordination layer.
The following capabilities represent architectural directions for further research. They should not be interpreted as claims that AEOS QUANTUM currently implements them or has independently validated them.
10.1 Evidence coordination
An enterprise may receive evidence from identity providers, AI agents, workflow platforms, cloud infrastructure, business applications, monitoring systems, and security tools. A future AEOS QUANTUM architecture could coordinate references to this evidence and preserve the relationship between each item, the relevant operation, and the enterprise policy under which the operation was authorized. The underlying systems would continue to provide evidence within their respective areas of responsibility. AEOS QUANTUM should not claim direct knowledge of facts that its evidence sources cannot establish.
10.2 Claim-specific assessment
A potential design direction is to associate each operational claim with explicit verification criteria. A claim that a workflow terminated would have different requirements from a claim that every identified downstream effect was resolved. This separation could help prevent a successful result at one layer from being incorrectly interpreted as proof of a broader outcome. The criteria would need to be defined for the relevant enterprise context.
10.3 Uncertainty and exception handling
An enterprise control architecture should not conceal uncertainty behind a single status indicator. A future design could distinguish missing evidence, conflicting records, incomplete coverage, and unresolved operations. This would help make uncertainty visible so that authorized personnel can determine whether further evidence, investigation, or remediation is required.
10.4 Human authority and accountability
Evidence does not eliminate the need for legitimate authority. A system may establish that a condition has been met without being authorized to determine every consequential response. For example, evidence may establish that a workflow remains unresolved. Whether to retry, cancel, compensate, escalate, or authorize another operation depends on the applicable policy, operational context, and delegated authority. This distinction reinforces the core AEOS principle: Capability ≠ Authority. The ability to analyze evidence does not automatically confer permission to make every consequential decision.
The intended operating principle remains: Autonomous where authorized. Human where required.
10.5 Vendor independence
The evidence coordination problem also reinforces the importance of avoiding unnecessary dependence on a single AI provider or enterprise application. A future architecture should aim to work with evidence from different systems wherever appropriate interfaces, permissions, and technical capabilities permit. This does not mean that every provider offers equivalent evidence or that every integration is interchangeable. It means that the enterprise control architecture should not automatically treat one vendor's internal report as the only possible source of truth when other relevant evidence is required and available. The long-term architectural objective is coordinated assurance across the enterprise—not the replacement of every underlying system by AEOS QUANTUM.
11. WHAT THE TRUST CHAIN ASSURANCE MODEL DOES NOT CLAIM
A serious research proposal must define its boundaries. The proposed Trust Chain Assurance Model does not claim: - That every enterprise event can be observed. - That cryptographic integrity guarantees the truth of a recorded statement. - That multiple records automatically constitute independent corroboration. - That event correlation proves causation. - That a verified workflow state proves every downstream effect has been resolved. - That an enterprise can always establish the absence of all relevant activity. - That one evidence status can represent every dimension of operational risk. - That AEOS QUANTUM currently implements the complete model. - That the model is an established industry standard or independently validated methodology.
The framework is a conceptual synthesis intended to structure a difficult operational question. Its value must ultimately be assessed through further technical analysis, domain-specific verification criteria, implementation experience, and independent evaluation. The framework also does not replace existing security, governance, monitoring, workflow, identity, or audit technologies. Those systems remain important sources of control and evidence. The research question is how an enterprise might coordinate their outputs into a defensible conclusion without overstating what those outputs establish.
12. OPEN RESEARCH QUESTIONS
Several questions remain unresolved and warrant further investigation.
12.1 How should evidence completeness be assessed?
An enterprise may know which sources it expected to receive evidence from without knowing whether those sources captured every relevant event. Further research is needed into practical ways of representing collection gaps, coverage assumptions, asynchronous processing, and dependencies between evidence sources.
12.2 How should independence be evaluated?
Two records may originate from different systems while depending on the same underlying data or event. An assurance process must distinguish genuine corroboration from duplicated reporting and shared-source dependence.
12.3 How should conflicting evidence be resolved?
When two systems disagree, the correct response cannot always be determined by selecting the newest record or the system with the most convenient interface. Resolution may require source-specific authority rules, reconciliation procedures, additional observations, or human investigation.
12.4 How should assurance work across organizational boundaries?
A distributed workflow may involve external providers whose internal execution states are not fully visible to the enterprise. The organization may be able to verify that a request was accepted without being able to verify its ultimate completion. Research must address how assurance statements should represent these boundaries without converting uncertainty into an unsupported claim.
12.5 How should evidence age affect assurance?
A record may have been accurate when collected but may no longer represent the current state. The relevant freshness requirement depends on the claim, the rate at which the underlying state can change, and the consequences of relying on stale information. A verified historical state should not automatically be presented as a verified current state.
12.6 Who is accountable for accepting residual uncertainty?
Technical evidence can inform a decision, but it cannot independently determine every acceptable level of risk. Organizations need clear responsibility for deciding when evidence is sufficient, when an operation must remain on hold, and when additional investigation is required. This is not merely a technical design question but also a question of enterprise governance and delegated authority.
13. CONCLUSION: FROM SAFE STATE TO JUSTIFIED ASSURANCE
The research progression from #062 through #064 can be summarized in three questions:
- **#062 — The Containment Gap:** Does revoking authority establish that autonomous execution is contained?
- **#063 — After Revocation: The Safe-State Problem:** Does stopping or restricting execution establish that the resulting operational state is known and resolved?
- **#064 — The Trust Chain Problem:** Does the available evidence justify the enterprise's conclusions about what happened?
Each question addresses a different layer of the same broader challenge. Enterprises need to understand not only what their autonomous systems are permitted to do but also what they have done, what effects remain, and what can reasonably be established from the available evidence.
No single log, agent report, cryptographic record, or monitoring dashboard should automatically be treated as a complete representation of enterprise truth. Each provides a particular view, with its own scope and limitations. The challenge is to connect those views without concealing uncertainty or claiming more than the evidence supports.
For AEOS QUANTUM, this research identifies a potential architectural direction: coordinating authority context, execution records, business-effect evidence, verification criteria, and accountable decisions across heterogeneous enterprise systems. Such a direction must preserve the distinction between what a source reports, what the evidence supports, and what an authorized decision-maker is entitled to conclude. It must also preserve the limitations of each source and the responsibility of the people and organizations that accept the resulting assessment.
The ultimate objective is not to make autonomous systems appear infallible but to help enterprises govern them without confusing capability with permission, activity with outcome, or evidence with certainty. Trustworthy autonomous execution requires more than a record of what a system did. It requires a defensible relationship between the authorized operation, the observed events, the resulting business effects, the evidence supporting the assessment, and the authority responsible for accepting the conclusion.
This is not a promise of absolute proof. It is a commitment to more precise claims, more accountable evidence, and more transparent uncertainty. The next frontier is not simply collecting more evidence. It is establishing who can verify a claim, under which criteria, within what scope, and with what accountability when the evidence remains incomplete. That is the Trust Chain Problem. Addressing it will require more than intelligence. It will require disciplined evidence, explicit authority, operational coordination, and a clear understanding of what an enterprise can—and cannot—claim to know.
RESEARCH STATUS & EVIDENCE DISCIPLINE
This publication distinguishes among documented facts, observations, analysis, proposed frameworks, and projections. The Trust Chain Assurance Model is a proposed conceptual framework for further research. It is not presented as an established industry standard, a completed technical specification, or a validated production methodology. Descriptions of AEOS QUANTUM refer to architectural direction and intended design. They should not be interpreted as claims of completed implementation, production performance, independent validation, or certification. The cited governance and provenance resources provide relevant foundations for the discussion. They do not independently validate the proposed AexoreX framework.
Sources and attribution
- AexoreX Systems Research; NIST AI RMF 1.0; NIST AI 600-1; IETF Datatracker — Verifiable AI Provenance Framework (VAP); AexoreX Newsroom #062 and #063. · statement link
About the author
Research desk of AexoreX Newsroom.
More from AexoreX Research Desk →Related stories
- Governing Autonomous Execution: Enterprise Control Planes and the Shift to Digital Labor
- The Non-Human Authorization Crisis: Re-Architecting Identity, Governance, and Execution for Autonomous Enterprise Systems
- AexoreX Systems Defines the Enterprise Intelligence Control Plane for the Autonomous Enterprise
- AexoreX Systems Introduces AEOS Enterprise Authority™ as Governance Layer for Autonomous Enterprise Intelligence
- Enterprise Intelligence Infrastructure and Governed Autonomy: The Architectural Foundation for the Autonomous Enterprise
- Governing Digital Labor: Bridging Capability and Authority in Autonomous Enterprise Architecture
- AFTER REVOCATION: THE SAFE-STATE PROBLEM IN AUTONOMOUS ENTERPRISE EXECUTION