Authority Continuity: The Missing Runtime Contract for Autonomous Enterprise Operations
Why AI Agents Need More Than Identity, Permissions, and Audit Logs
Series: Enterprise Intelligence Infrastructure Research Domain: Enterprise Intelligence Infrastructure for Autonomous Enterprises Publication Date: October 18, 2026 Estimated Reading Time: 18–22 minutes Article Type:…
Opinion · AI-assisted, human edited
Series: Enterprise Intelligence Infrastructure Research Domain: Enterprise Intelligence Infrastructure for Autonomous Enterprises Publication Date: October 18, 2026 Estimated Reading Time: 18–22 minutes Article Type: Research & Analysis Author: AexoreX Research Desk
Executive Summary AI agents are becoming capable of doing more than answering questions. They can work with business applications, access information, update records, and carry out tasks across connected systems. These abilities create new opportunities for businesses. They also raise an important question: How can an enterprise ensure that an AI agent still has valid authority when it performs an action? An agent may have the correct identity and the required technical permissions. However, the business situation may have changed since those permissions were granted. A manager may withdraw an approval. A company may change its purchasing rules. A project may end. A financial risk may increase. Yet a connected system may still rely on an earlier decision. This problem connects directly to the Authority Drift Problem discussed in AexoreX Newsroom #073. That earlier article examined what happens when the rules enforced by a system no longer match current business decisions. This article takes the next step: examining how authority can remain valid, limited, and verifiable throughout an operation. We call this proposed analytical concept Authority Continuity. Authority Continuity means maintaining a reliable connection between an approved business decision and the actions performed under that decision, including when circumstances change. It asks whether an action can be linked to: The person or system that initiated it. The business purpose behind it. The authority under which it was requested. The rules and conditions that apply. The evidence used to approve or permit it. The result of the action. Any required stop, review, recovery, or reconciliation process. This is not simply a question of access control. It is a question of whether authority remains valid throughout the work. This article proposes Authority Continuity as a design principle for autonomous enterprise operations. It does not present the term as an established industry standard, nor does it claim that every enterprise requires a separate system with this name. The central argument is straightforward: An AI agent should not continue acting merely because it received permission earlier. Its authority must remain valid for the action it is about to perform.
1. From Authority Drift to Authority Continuity In #073, The Authority Drift Problem: When Runtime Enforcement No Longer Matches Business Intent, we examined a gap between current business decisions and the rules that enterprise systems continue to enforce. Consider a simple example. A company allows an AI agent to prepare supplier orders. Orders above a certain value require human approval. Later, the company changes its purchasing policy because of a new financial risk. The updated policy reaches one application, but another connected system continues using the previous rule. The agent submits an order based on its existing permissions. The system may have followed the rules it was given. Yet those rules may no longer reflect the company's current decision. This is authority drift: a growing difference between the authority assigned to a system and the authority that should apply under current business conditions. Authority Continuity addresses the next question. Once a business decision grants authority, how can the enterprise ensure that the authority remains valid as work moves across systems, policies, people, and changing conditions? The distinction is important. Concept Main question Runtime Authority Is this action permitted at the moment of execution? Authority Drift Do the enforced rules still match the current business decision? Authority Continuity Does valid authority remain connected to the action throughout the operation?
These concepts are related, but they are not identical. Runtime authority focuses on permission at the point of action. Authority drift focuses on changes that make previously assigned authority unsuitable. Authority continuity focuses on preserving and checking the connection between approved authority and actual execution as an operation progresses. The proposed relationship is therefore: Runtime Authority → Authority Drift Detection → Authority Continuity This is a conceptual sequence, not a required industry architecture. An enterprise may address these concerns through existing identity systems, policy engines, workflow controls, application logic, and monitoring tools. The objective is not to create another layer of complexity without reason. The objective is to make sure that an action remains connected to the right decision.
2. Identity, Permission, and Authority Are Different To understand Authority Continuity, we must first separate three ideas that are often treated as if they mean the same thing. Identity: Who or what is acting? Identity helps an enterprise identify a person, service, application, or AI agent. For example, a business system may recognize an AI agent using a specific service identity. This is an essential starting point. Without reliable identification, the enterprise may not know which system requested an action. However, knowing the identity does not automatically establish that every requested action is allowed. Permission: What can the system access? Permissions define the resources and operations available to an identity. An AI agent may be allowed to read supplier records, create purchase requests, or update selected fields in a business application. These permissions help limit what the agent can technically do. But technical access does not automatically establish that an action is appropriate in every business situation. An agent may have permission to create a purchase request without having authority to approve the purchase. Authority: What is the system allowed to do under the current conditions? Authority connects an action to an approved purpose, decision, responsibility, and set of conditions. For example, an AI agent may be authorized to prepare a supplier order under an approved purchasing process. That authority may depend on several conditions: The supplier is approved. The order is within the permitted scope. The required budget remains available. The relevant approval is still valid. No policy change has suspended the operation. The action does not exceed the agent's assigned responsibility. These conditions may vary between enterprises and workflows. The key point is that identity, permission, and authority answer different questions. An identity can be valid while a permission is too broad. A permission can be technically active while the business approval behind an action is no longer valid. An action can also be approved in principle but still fail a required execution check. Capability enables action. Permission provides technical access. Authority determines whether the action is allowed under the applicable conditions. Reliable enterprise automation must account for all three.
3. Why Existing Security Controls Are Not Enough on Their Own Authority Continuity does not replace existing security controls. It builds on the problems those controls are designed to address. Several established technologies already support important parts of this challenge. Identity and access management Identity and access management systems help organizations identify users and systems, assign permissions, and control access to resources. They are essential for limiting access and managing responsibilities. However, enterprises must also ensure that changes in roles, business rules, and approvals reach every relevant part of an operation. The exact solution depends on the systems involved and how their policies are managed. Zero Trust The National Institute of Standards and Technology (NIST) describes Zero Trust Architecture in its publication SP 800-207. Zero Trust does not assume that a user or system should automatically be trusted simply because it is inside an organization's network. Access decisions should consider the relevant identity, resource, and conditions. This provides an important security foundation. Authority Continuity raises a related question: how can an enterprise ensure that the business decision behind an action remains valid as circumstances change? Zero Trust and Authority Continuity should not be treated as competing approaches. They address related but different design concerns. Token revocation and token checks OAuth provides mechanisms for managing access tokens. For example: RFC 7009 — OAuth 2.0 Token Revocation describes a standard method for revoking tokens. RFC 7662 — OAuth 2.0 Token Introspection defines a method for checking information about an access token, including whether it is active. RFC 8693 — OAuth 2.0 Token Exchange defines a protocol for exchanging security tokens, including tokens used for impersonation and delegation. These standards support important identity and access-management functions. However, they do not automatically guarantee that every business decision behind an action remains valid throughout a complex workflow. For example, an access token may remain active even though a manager has withdrawn a specific business approval. Whether the action is blocked depends on how the enterprise connects its approval process to its execution controls. The important distinction is this: A valid token is evidence of an access-related condition. It is not, by itself, proof that every business condition for an action has been satisfied. AI risk management The NIST AI Risk Management Framework provides guidance for organizations that design, develop, deploy, or use AI systems. Its broader risk-management approach can help enterprises assess the risks of giving AI agents access to business systems and allowing them to perform tasks. Authority Continuity can be considered a proposed design principle within an organization's broader approach to AI governance and operational risk management. This article does not claim that NIST formally defines Authority Continuity as a separate category. The practical lesson is that existing controls remain essential, but they must work together with current business decisions and suitable execution checks.
4. How Authority Can Be Lost During an Operation Authority problems do not always begin with a major security incident. They can develop when an operation continues while the conditions that justified it are changing. Consider the following example. A company allows an AI agent to process routine supplier orders. The agent operates within a defined scope and follows the company's purchasing rules. The workflow begins normally. The agent identifies a supplier, prepares an order, checks the available information, and sends the request to the relevant system. Then the situation changes. A manager suspends the supplier because of a new compliance concern. The suspension reaches the supplier-management system, but the purchasing workflow does not receive the update immediately. The agent continues processing the order. Several outcomes are possible, depending on the system design. The order may be blocked by a later check. It may be sent for human review. It may already have reached another system. Or the enterprise may discover the issue only during reconciliation. The example illustrates five important stages. Stage 1: Authority is granted A business decision allows the agent to perform a defined task. The authority should have a clear purpose and scope. Stage 2: Work begins The agent performs actions under the original decision. Each step may involve a different application, service, or approval process. Stage 3: Conditions change A supplier is suspended, a budget changes, an approval is withdrawn, or a policy is updated. The earlier authority may no longer be suitable. Stage 4: The change must reach the relevant controls The enterprise must determine how the updated decision affects work that is waiting, running, or moving between systems. A policy update in one location may not automatically stop an action elsewhere. Stage 5: The operation must respond Depending on the situation, the system may need to block the next action, pause the workflow, request a new approval, cancel a pending request, or escalate the issue. If an action has already taken effect, the enterprise may also need a separate recovery or reconciliation process. The important point is that stopping future activity and reversing a completed action are different problems. A well-designed system should not assume that revoking authority automatically reverses every previous action. It must identify what has already happened and determine the appropriate response.
5. What Authority Continuity Means in Practice For this article, Authority Continuity is a proposed analytical concept for maintaining a verifiable connection between approved authority and the actions performed under it throughout an operation. It does not mean that authority can never change. Business decisions must be able to change. Permissions must be adjustable. Approvals must be withdrawable. Workflows must be able to stop when necessary. Continuity means that these changes are managed in a way that preserves the connection between the current decision and the action being performed. A practical approach should address six questions. 1. Who initiated the action? The enterprise should be able to identify the person, agent, application, or workflow that initiated the request. Where an agent acts on behalf of a person or another system, that relationship should be recorded when relevant. 2. What business purpose was approved? The enterprise should know why the action was permitted. A general permission such as “can update records” may be insufficient to explain why a particular update was allowed. The required detail depends on the action's importance and risk. 3. What conditions applied? The system should identify the relevant rules, approvals, limits, and business conditions. For example, an order may be permitted only for an approved supplier and within a defined budget. 4. Are those conditions still valid? Before a consequential action occurs, the system should check the conditions that matter to that action. Some information can be checked when a workflow begins. Other information may need to be checked again immediately before execution. The correct timing depends on how quickly conditions can change and how serious the consequences could be. 5. What happened? The enterprise should retain suitable evidence of the decision, relevant checks, execution attempt, and result. This evidence helps people investigate errors and understand whether the system followed the expected process. 6. What happens if authority changes? The enterprise should define how the operation responds when an approval is withdrawn, a policy changes, or a required condition is no longer satisfied. Possible responses include stopping, holding, requesting approval, escalating to a human, or beginning a controlled recovery process. These responses should be defined before they are needed.
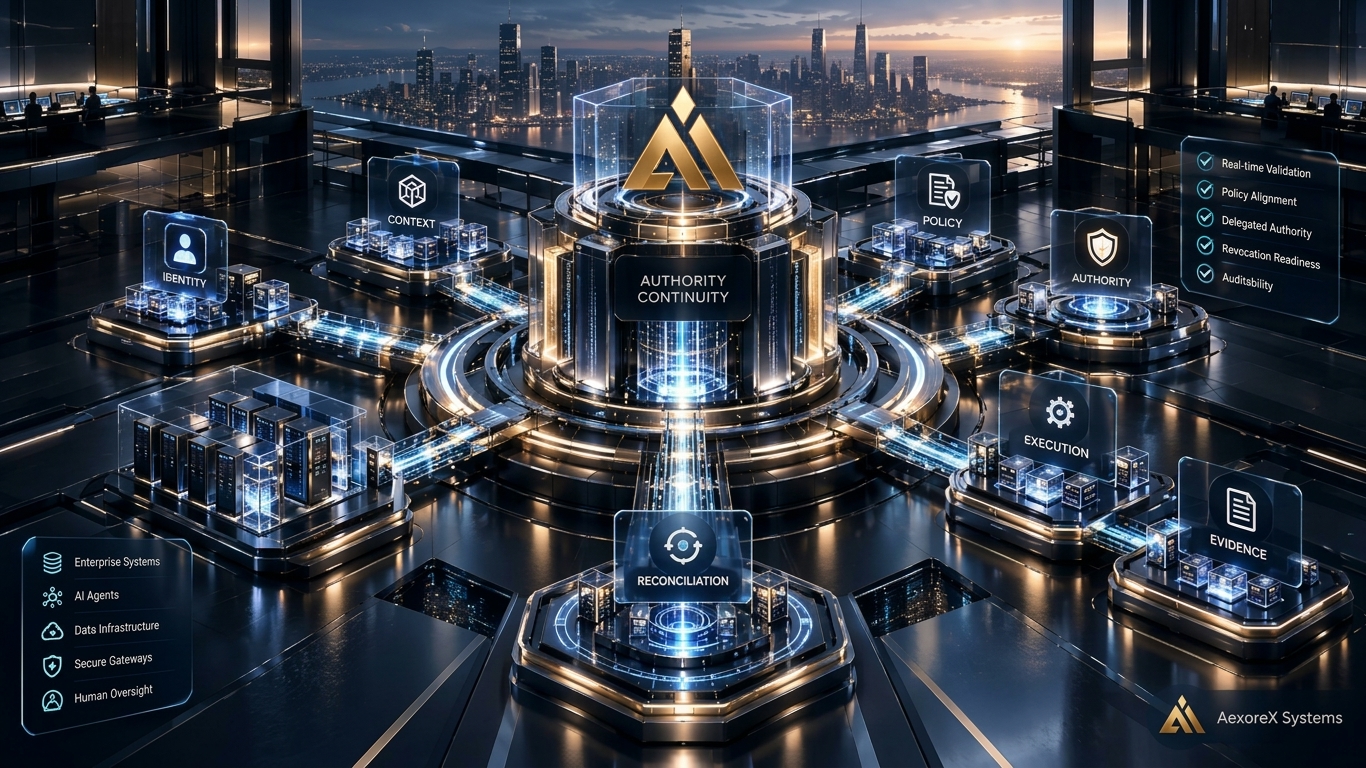
6. A Proposed Authority Continuity Model To make the concept easier to apply, this article proposes the following model: Identity → Context → Policy → Authority → Execution → Evidence → Reconciliation This is an analytical framework proposed by AexoreX Research Desk. It is not an established industry standard, and it does not require every enterprise to implement seven separate systems. The stages describe the questions that should be addressed during a controlled operation. Identity Identify the person, agent, service, or application involved. Context Understand the business situation in which the action is requested. Context may include the task, relevant records, current status, and information that affects the decision. Policy Identify the applicable rules, limits, and conditions. The enterprise should know which policy applies and who is responsible for maintaining it. Authority Determine whether the requested action is allowed under the current decision and conditions. This may involve an existing approval, a defined role, a spending limit, or another form of delegated authority. Execution Allow the action only through controls appropriate to its risk. A system should not rely solely on an AI agent's own statement that it is authorized. Where the risk justifies it, an independent control should check the action before it reaches the relevant business system. Evidence Record the information needed to understand what was requested, which controls applied, what decision was made, and what result followed. Evidence should be useful for review without collecting unnecessary sensitive information. Reconciliation Compare the intended result with the actual state of the business system. If something went wrong, the enterprise should determine what happened and who or what is allowed to resolve the issue. Reconciliation is especially important when an operation involves several systems that may not update at the same time. The stages are connected, but they are not always strictly sequential. Some checks may be repeated, and some may occur in parallel. The purpose is not to force every workflow into a rigid pattern. It is to ensure that important authority questions are not overlooked.
7. Authority Continuity Across Connected Systems Enterprise operations rarely take place in a single application. A purchase request, for example, may involve a procurement platform, a supplier database, a financial system, an approval workflow, and an inventory service. An AI agent may interact with several of these systems during one task. This creates a challenge: the authority that permits one step may not automatically permit every later step. An agent may be allowed to prepare a purchase request but not approve it. Approval may permit the purchase but not permit a change to the supplier's bank details. A financial system may accept a payment request, but the enterprise may still need to confirm that the supplier and transaction satisfy current business requirements. Each step must respect the authority applicable to that action. The problem of changing context Suppose an agent starts a workflow when all required conditions are satisfied. During the workflow, a key condition changes. The system must decide whether the original approval still applies, whether another check is needed, or whether the operation must stop. There is no universal answer for every business process. Some decisions remain valid for a defined period. Others must be checked again before execution. High-risk actions may require renewed approval when important conditions change. The enterprise should define these rules according to the action's risk and the consequences of an incorrect decision. The problem of delegated authority Delegation adds another question. If a person authorizes an agent to perform a task, and that agent asks another service to complete part of the task, what authority does the second service receive? The answer should not be assumed. The enterprise needs a clear way to define which actions are permitted, which limits apply, and whether further delegation is allowed. The agent's technical ability to call another service should not automatically expand its business authority. This is one reason why delegated identity, access controls, and execution checks must be designed together. The problem of partial completion A workflow may complete some steps before another step fails. For example, a purchase request may be recorded in one application but rejected by a connected financial system. The enterprise should not treat the entire operation as successful simply because one component returned a successful response. It must determine the actual state of the operation and decide whether to retry, stop, compensate for an earlier action, or request human review. Authority Continuity therefore connects authorization with execution evidence and reconciliation. A workflow is not fully controlled simply because its first action was approved.
8. Revocation Must Lead to a Defined Response Authority can change during an operation. An approval may be withdrawn. An agent's assignment may end. A supplier may be suspended. A security concern may require a workflow to stop. Revocation is important, but the enterprise must define what revocation means for work already in progress. Consider four situations. Situation A: The action has not started The system may be able to block the action before it begins. This is often the simplest case, provided the relevant control receives the updated decision in time. Situation B: The action is waiting for approval The workflow may be held or cancelled according to the business rules. The system should avoid treating an earlier request as permanently approved if the approval conditions have changed. Situation C: The action is in progress The system may need to stop further steps, prevent additional requests, or move the operation into a controlled hold state. Stopping safely can be more complex when a connected service is already processing a request. Situation D: The action has already taken effect The action may not be reversible. A payment may have been completed, a record may have been sent to another organization, or an external process may already have started. In such cases, revocation alone cannot undo the outcome. The enterprise may need a separate process for correction, compensation, investigation, or reconciliation. These differences matter because revoking authority is not the same as reversing an action. A mature design should define the expected response for each important class of operation. It should also establish who is allowed to decide what happens when the correct response is uncertain. For high-impact decisions, the system should be able to hold the operation and ask for human review rather than inventing a response.
9. Evidence Must Explain the Decision, Not Just Record the Event Many systems produce logs. A log may show that an agent called an API, updated a record, or received a successful response. That information is useful, but it may not answer the most important questions. Why was the action permitted? Which approval applied? What policy was used? Was a relevant condition checked before execution? Had the authority changed? What did the system do when it detected the change? These questions require evidence that connects the decision to the action. For a consequential operation, useful evidence may include: The identity of the initiating person, agent, or service. The action requested and its business purpose. The relevant approval or delegation. The applicable policy or decision version. The checks performed before execution. The decision to allow, hold, block, or escalate. The execution result. Any subsequent correction or reconciliation. Not every operation needs the same level of detail. A routine, low-risk action may require less evidence than a financial transfer or a change to a critical business record. Evidence collection should be proportionate to risk and should follow the organization's privacy, security, and retention requirements. Sensitive data should not be collected simply because it might be useful someday. The goal is to preserve enough reliable information to explain what happened and support appropriate review. This also requires care with the meaning of evidence. A log entry does not automatically prove that an action was correct. A successful API response does not necessarily prove that the business outcome was correct. A recorded approval does not necessarily prove that all required conditions remained valid. Evidence becomes useful when it is connected to a clear decision process and the actual result.
10. A Proposed Authority Continuity Plane The model above describes the questions an enterprise should answer. A further architectural question follows: How can an enterprise coordinate these checks across different applications, agents, and business processes? This article proposes the term Authority Continuity Plane for a possible architectural layer that helps coordinate authority-related decisions and evidence across an enterprise. The term is a proposed AexoreX architectural concept. It is not an established industry category, a recognized standard, or a claim that AEOS QUANTUM already provides this capability. Depending on an enterprise's existing architecture, the relevant functions could be implemented through a combination of existing identity systems, policy engines, workflow platforms, approval services, execution gateways, and evidence systems. The proposed plane would help coordinate seven functions. 1. Identity and delegation Establish which person, agent, or service initiated the action and what delegation applies. 2. Context management Identify the business conditions that matter to the requested action. 3. Policy evaluation Determine which rules and limits apply to the operation. 4. Authority validation Check whether the action is allowed under the current decision and required conditions. 5. Execution control Ensure that consequential actions pass through appropriate enforcement points. 6. Evidence collection Record enough information to support investigation, review, and accountability. 7. Revocation and reconciliation Help the enterprise respond when authority changes and determine the actual state of the operation. These functions do not necessarily require a single centralized product. In some environments, central coordination may be appropriate. In others, a distributed design may better fit performance, availability, security, or regulatory requirements. The important requirement is not that every function belongs to one component. It is that the enterprise can explain how the functions work together and where responsibility lies when they do not. A proposed Authority Continuity Plane should therefore be evaluated by its actual controls, evidence, failure behavior, and operational limits—not by its name.
11. Human Oversight and the Limits of Autonomy Authority Continuity does not mean that humans must approve every AI action. That would remove many of the benefits of automation. The better approach is to match the level of control to the importance and risk of the action. A low-risk task may be performed automatically within a clearly defined scope. A more consequential action may require additional checks. An action with significant financial, legal, security, or operational consequences may require explicit human approval. The enterprise should decide these requirements based on its own risks, responsibilities, and applicable rules. Three principles are especially important. Autonomy must have boundaries An agent should operate within a defined scope. It should not gain additional authority simply because it can access another application or call another service. Uncertainty should trigger a defined response When a required condition cannot be verified, the system should follow a clear rule. Depending on the action, that may mean stopping, holding, requesting approval, or escalating to a responsible person. The system should not silently treat missing information as approval. Human authority must remain clear The enterprise should identify who can grant authority, change its limits, withdraw approval, and resolve important exceptions. Human oversight is meaningful only when responsibilities are clear and the relevant controls can carry out those decisions. This is especially important when several agents or services participate in the same operation. The goal is not maximum autonomy. The goal is dependable autonomy within approved boundaries.
12. How Enterprises Can Begin Organizations do not need to redesign every business system to begin addressing Authority Continuity. A practical starting point is to identify a small number of important workflows and examine how authority is managed from beginning to end. Step 1: Select a consequential workflow Choose an operation where an incorrect action could create a meaningful financial, security, legal, or operational impact. Examples may include supplier payments, account changes, customer-data updates, or approval workflows. The first workflow should be narrow enough to examine carefully. Step 2: Map the authority behind each action Identify who or what can initiate, approve, execute, and change the operation. Record the permissions and business conditions that apply. Pay particular attention to actions that cross system boundaries. Step 3: Identify what can change Determine which events may make existing authority invalid. These may include an approval being withdrawn, a role changing, a policy being updated, a supplier being suspended, or a risk condition being triggered. Step 4: Decide when checks are required Some conditions may be checked at the beginning of the workflow. Others may need to be checked again immediately before an important action. The timing should reflect the risk of the action and how quickly relevant conditions can change. Step 5: Define stop and escalation behavior Decide what the system should do when authority is missing, withdrawn, unclear, or inconsistent across connected systems. Document which situations can be handled automatically and which require human review. Step 6: Connect execution with evidence Ensure that the enterprise can explain why an action was permitted and what happened afterward. The evidence should be suitable for the workflow's risk level and should respect privacy and security requirements. Step 7: Test failure scenarios Do not test only the normal path. Examine what happens when an approval is withdrawn, a policy update arrives late, a connected service becomes unavailable, or an operation stops after completing only part of its work. A design that works only when every system behaves as expected may be unsuitable for important enterprise operations. Step 8: Review the results Evaluate whether the controls worked as intended. Useful questions include: Could the system identify the authority behind an action? Did it detect relevant changes before the action occurred? Did it stop or escalate when required? Could the enterprise determine what had already happened? Was the final business state clear? Were the results supported by reliable evidence? The answers will help the organization identify where additional controls are needed. This approach makes Authority Continuity a practical design and evaluation topic rather than an abstract promise.
13. The Next Five, Ten, and Fifteen Years The future of autonomous enterprise operations is uncertain. The following scenarios are possibilities, not predictions or statements of established fact. Their likelihood will depend on technical progress, industry standards, regulation, business needs, and the ability of organizations to manage operational risk. The Next Five Years: Better Control of Individual Agents Enterprises may place greater emphasis on identifying AI agents, limiting their permissions, managing delegation, and recording consequential actions. More organizations may connect AI agent governance with existing identity, security, and workflow controls. The main challenge will be making these controls work consistently across different applications and services. Organizations will also need to decide which actions can be performed automatically and which require additional approval. The Next Ten Years: More Coordination Across Enterprise Workflows If AI agents become more deeply integrated into business operations, some enterprises may need stronger ways to coordinate authority across multi-step workflows. A decision made in one system may affect what another system or agent is allowed to do. This could increase demand for clear delegation rules, shared policy information, consistent execution checks, and evidence that can be reviewed across system boundaries. The challenge will not be solved simply by giving every agent a unique identity. Enterprises will also need to manage how authority changes as work moves between people, agents, and services. The Next Fifteen Years: Authority as a Core Enterprise Design Concern If autonomous operations become common across complex enterprises, authority management may become a more visible part of enterprise architecture. Organizations may evaluate systems not only by their ability to perform tasks, but also by their ability to explain, limit, stop, and review those tasks. This could encourage closer coordination between business governance, identity management, AI risk management, execution controls, and operational evidence. However, the specific architectures and standards that emerge remain uncertain. Authority Continuity may prove useful as an analytical concept, but its long-term value will depend on whether it helps enterprises identify and solve real problems. The important question is not whether a new term becomes popular. It is whether the underlying control problem is understood and managed effectively.
14. The Strategic Implication for Enterprise Intelligence Infrastructure Enterprise intelligence is not only about making better decisions. It is also about connecting decisions to actions in a way that respects business rules, responsibilities, and limits. An AI system may recommend a useful action. A workflow may approve it. An application may accept it. Yet the enterprise still needs to know whether the action was performed under valid authority and whether the result matches the intended outcome. This creates a broader architectural challenge. The enterprise must connect the information used to make a decision with the authority that permits the action, the controls that govern execution, and the evidence that explains the result. That connection becomes more important as operations involve more agents, applications, and automated steps. The proposed Authority Continuity concept offers one way to examine this challenge. It asks enterprises to look beyond individual permissions and consider the full relationship between decisions, conditions, execution, and outcomes. For AexoreX Systems, this is a research direction within the broader field of Enterprise Intelligence Infrastructure for Autonomous Enterprises. It is not a claim that one architectural model will solve every enterprise problem. Different organizations will require different controls, integrations, and levels of oversight. The value of the concept lies in providing a clear set of questions for evaluating whether autonomous operations remain connected to valid business authority.
Conclusion: Permission Must Remain Connected to the Decision Enterprise systems need identity, permissions, and runtime controls. These are essential foundations for secure and reliable automation. But a permission granted earlier does not automatically prove that an action remains appropriate later. Business conditions change. Approvals are withdrawn. Roles evolve. Policies are updated. Work moves between connected systems. Some actions complete before a problem is detected. Enterprises must therefore consider not only whether an action was initially authorized, but also whether the authority behind it remains valid as the operation progresses. This is the central idea behind the proposed Authority Continuity concept. Authority Continuity connects the business decision, the applicable conditions, the execution process, and the evidence of what happened. It also requires clear responses when authority changes or can no longer be verified. This does not mean that every action needs human approval. It means that autonomy should operate within defined and enforceable limits, with appropriate checks and a clear way to stop or review consequential actions. The concept also has practical limits. It cannot guarantee that every system receives an update instantly, that every action can be reversed, or that every business decision is correct. Those challenges require specific technical controls, operational processes, and human responsibility. The objective is to make those limits visible and manageable. As enterprises move toward more autonomous operations, dependable automation will require more than the ability to act. It will require a reliable connection between the authority granted, the conditions that apply, the action performed, and the result that follows. Capability enables action. Authority permits action. Evidence helps verify what happened. Continuity connects them throughout the operation. For autonomous enterprises, the next step is not simply to give AI agents more responsibility. It is to ensure that every consequential action remains connected to the right authority, under the right conditions, for the right purpose.
References and Further Reading The following sources support the established technical foundations discussed in this article. Authority Continuity and Authority Continuity Plane are proposed analytical and architectural concepts introduced in this article; they are not presented as terms formally defined by these sources. 1. National Institute of Standards and Technology (NIST) Zero Trust Architecture — NIST SP 800-207 https://csrc.nist.gov/pubs/sp/800/207/final Relevant to identity-aware access decisions and the principles of Zero Trust Architecture. 2. National Institute of Standards and Technology (NIST) Artificial Intelligence Risk Management Framework (AI RMF 1.0) https://www.nist.gov/itl/ai-risk-management-framework Provides guidance for identifying and managing risks related to AI systems. 3. Internet Engineering Task Force (IETF) RFC 7009: OAuth 2.0 Token Revocation https://www.rfc-editor.org/rfc/rfc7009 Defines a standard method for revoking OAuth access and refresh tokens. 4. Internet Engineering Task Force (IETF) RFC 7662: OAuth 2.0 Token Introspection https://www.rfc-editor.org/rfc/rfc7662 Defines a method for obtaining information about an OAuth token, including its active state. 5. Internet Engineering Task Force (IETF) RFC 8693: OAuth 2.0 Token Exchange https://www.rfc-editor.org/rfc/rfc8693 Defines a protocol for exchanging security tokens, including tokens used for impersonation and delegation. 6. National Institute of Standards and Technology (NIST) New Concept Paper on Identity and Authority of Software Agents — February 5, 2026 https://www.nist.gov/news-events/news/2026/02/new-concept-paper-identity-and-authority-software-agents Discusses identity and authorization considerations for software agents and AI agent applications. 7. National Institute of Standards and Technology (NIST) Announcing the AI Agent Standards Initiative for Interoperable and Secure Innovation — February 17, 2026 https://www.nist.gov/news-events/news/2026/02/announcing-ai-agent-standards-initiative-interoperable-and-secure Describes NIST's initiative concerning secure, interoperable AI agents and the development of relevant standards and protocols. 8. National Institute of Standards and Technology (NIST) Back to the Future: Why Agentic AI Needs a Strong Identity Foundation — August 27, 2026 https://www.nist.gov/blogs/cybersecurity-insights/back-future-why-agentic-ai-needs-strong-identity-foundation Discusses identity foundations and security challenges associated with agentic AI. Related AexoreX Research #071 — The Runtime Authority Problem: From Granted Permissions to Enforced Execution Boundaries https://news.aexorex.com/news/the-runtime-authority-problem-from-granted-permissions-to-enforced-execution-boundaries #073 — The Authority Drift Problem: When Runtime Enforcement No Longer Matches Business Intent https://news.aexorex.com/news/the-authority-drift-problem-when-runtime-enforcement-no-longer-matches-business-intent These articles provide the conceptual background for the discussion of runtime authority, changing business conditions, and the proposed Authority Continuity framework.
Editorial Note This article presents conceptual research and architectural analysis. The terms Authority Continuity and Authority Continuity Plane are proposed frameworks for discussion and further evaluation, not established industry standards. Examples are illustrative. The article does not claim that AexoreX Systems or AEOS QUANTUM™ has implemented, deployed, or independently validated all capabilities discussed. The technologies and standards referenced above support specific aspects of identity, access management, AI risk management, and token handling. They should not be interpreted as direct proof of the proposed framework as a whole. — AexoreX Research Desk The Intelligence, Research & Institutional Publication of AexoreX Systems
Sources and attribution
- AexoreX Research Desk — Original Research & Analysis · statement link
About the author
Research desk of AexoreX Newsroom.
More from AexoreX Research Desk →Related stories
- The Runtime Authority Control Plane: Why Enterprise AI Needs More Than Identity and Permissions
- The Non-Human Identity Control Plane: Dynamic Authority and Traceable Delegation for Autonomous Enterprise Operations
- The Identity-to-Execution Seam: Governing Non-Human Identities and Dynamic Delegation in Autonomous Enterprise Operations
- AexoreX Systems Introduces AEOS Enterprise Authority™ as Governance Layer for Autonomous Enterprise Intelligence
- From Digital Labor to Autonomous Enterprise Operations: Why an Intelligence Layer Matters
- From Enterprise Intelligence to Governed Autonomous Execution: The Next Step Toward the Autonomous Enterprises
- Financial Authority: Governing Autonomous Spending in the Agentic Enterprise
- The Infrastructure Behind the Autonomous Enterprise: Building the Foundation for Enterprise Intelligence
- Governing Digital Labor: Bridging Capability and Authority in Autonomous Enterprise Architecture
- #025 — The Enterprise AI Inflection Point: From AI Agents to Governed Autonomous Operations
- The Authority Drift Problem: When Runtime Enforcement No Longer Matches Business Intent